
Use cases · Security and IT
Make agentic product work governable and inspectable
Prodeology is designed so organizations can see what context an agent used, which action it proposed, where a person approved, and which external tool was involved.
Keep workspace context scoped
Product data and operations belong to a defined workspace and role context. Access decisions should be enforced at the boundary where work occurs.
How the work changes
Consequential work stops at a visible authority boundary before it proceeds.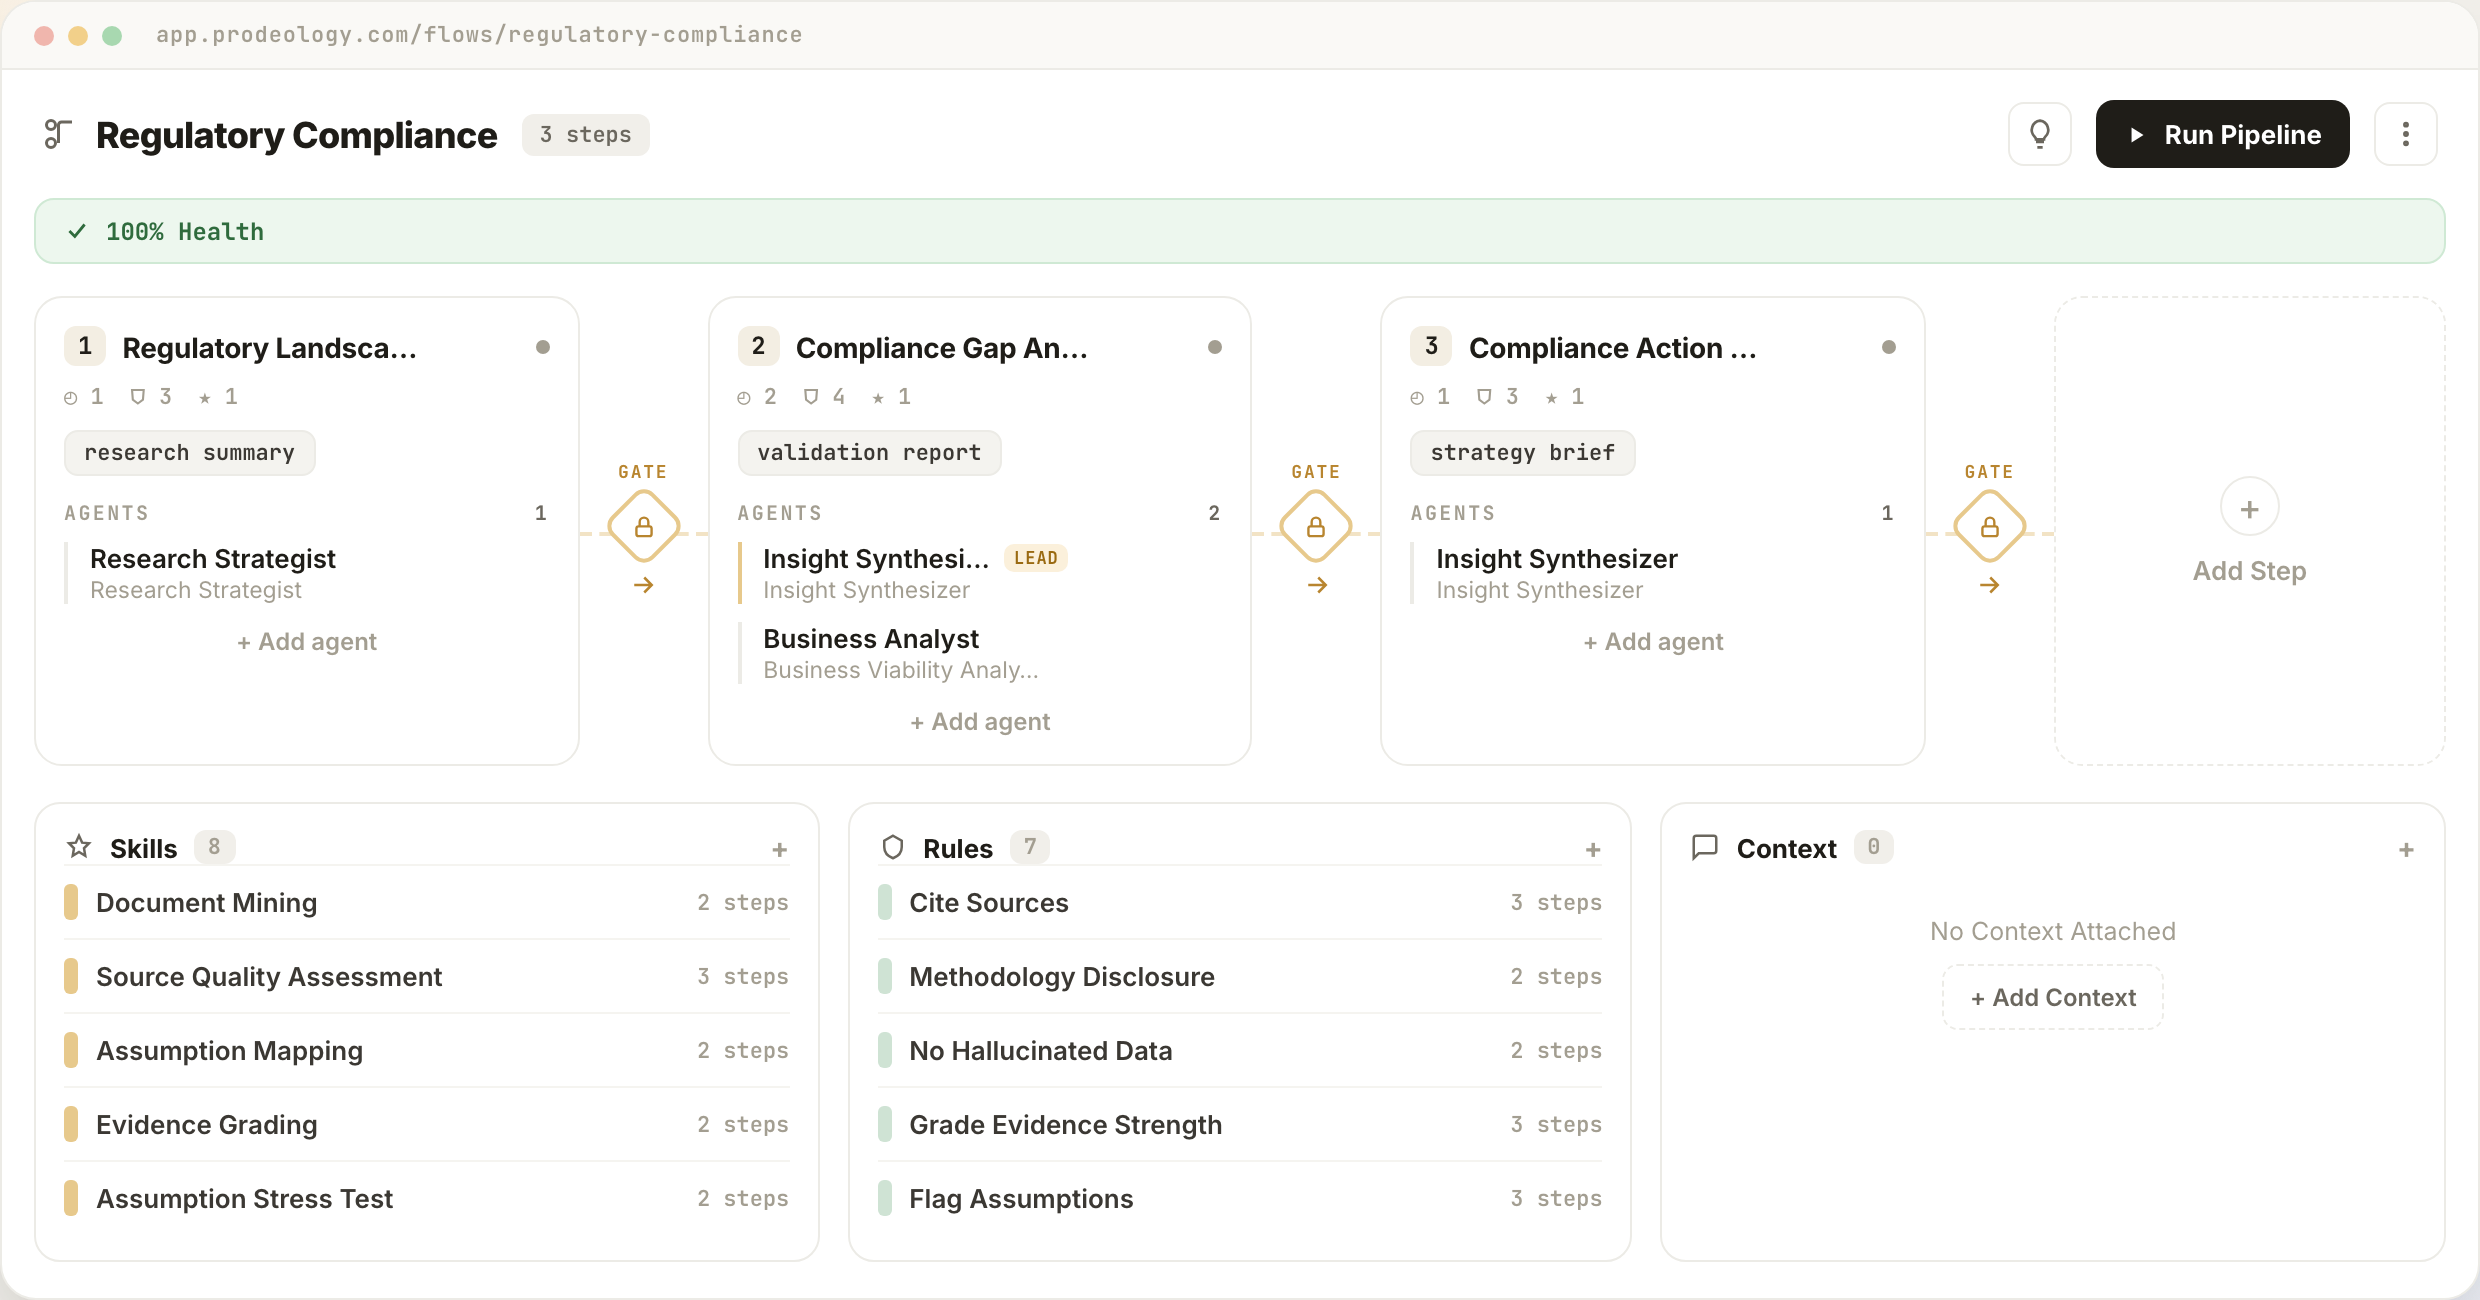
Make external actions explicit
Tool-backed workflows need validated inputs, truthful results, and clear failure reporting rather than optimistic claims that an action completed.
- Use least-necessary access
- Preserve action and decision trails
- Require approval where consequence warrants it
Inspect the operating model
Security and IT teams can evaluate agents, rules, tools, and human gates as a system rather than reviewing isolated prompts.
Review the full path of a sensitive action
Check who initiated the workflow, which workspace context was available, what tool permission was used, how inputs were validated, and where approval occurred. A prompt review alone cannot establish whether the resulting operation is safe.
Controls require correct configuration
Prodeology supports governed operation; it does not remove the need for identity policy, vendor review, data classification, or organization-specific security assessment.